GRC Platform for Autonomous Compliance: Continuous Without the Busywork
A GRC platform that replaces audit panic with continuous compliance. AI agents monitor, collect evidence, and remediate your controls 24/7: so your compliance posture is always current.
Trusted by 150+ enterprise customers worldwide
You Call It Compliance. Your Team Calls It Survival Mode
Months of business-as-usual, then six weeks of scrambling for screenshots and configs.
Compliance Theater
Point-in-time audits miss drift: pass on Tuesday, misconfigured S3 bucket on Wednesday.
The People Tax
Senior engineers spend each quarter gathering evidence and filling out spreadsheets.
Audit Roulette
You only review controls weeks before the auditor arrives, so findings are surprises.
From Static Snapshots to Continuous Compliance
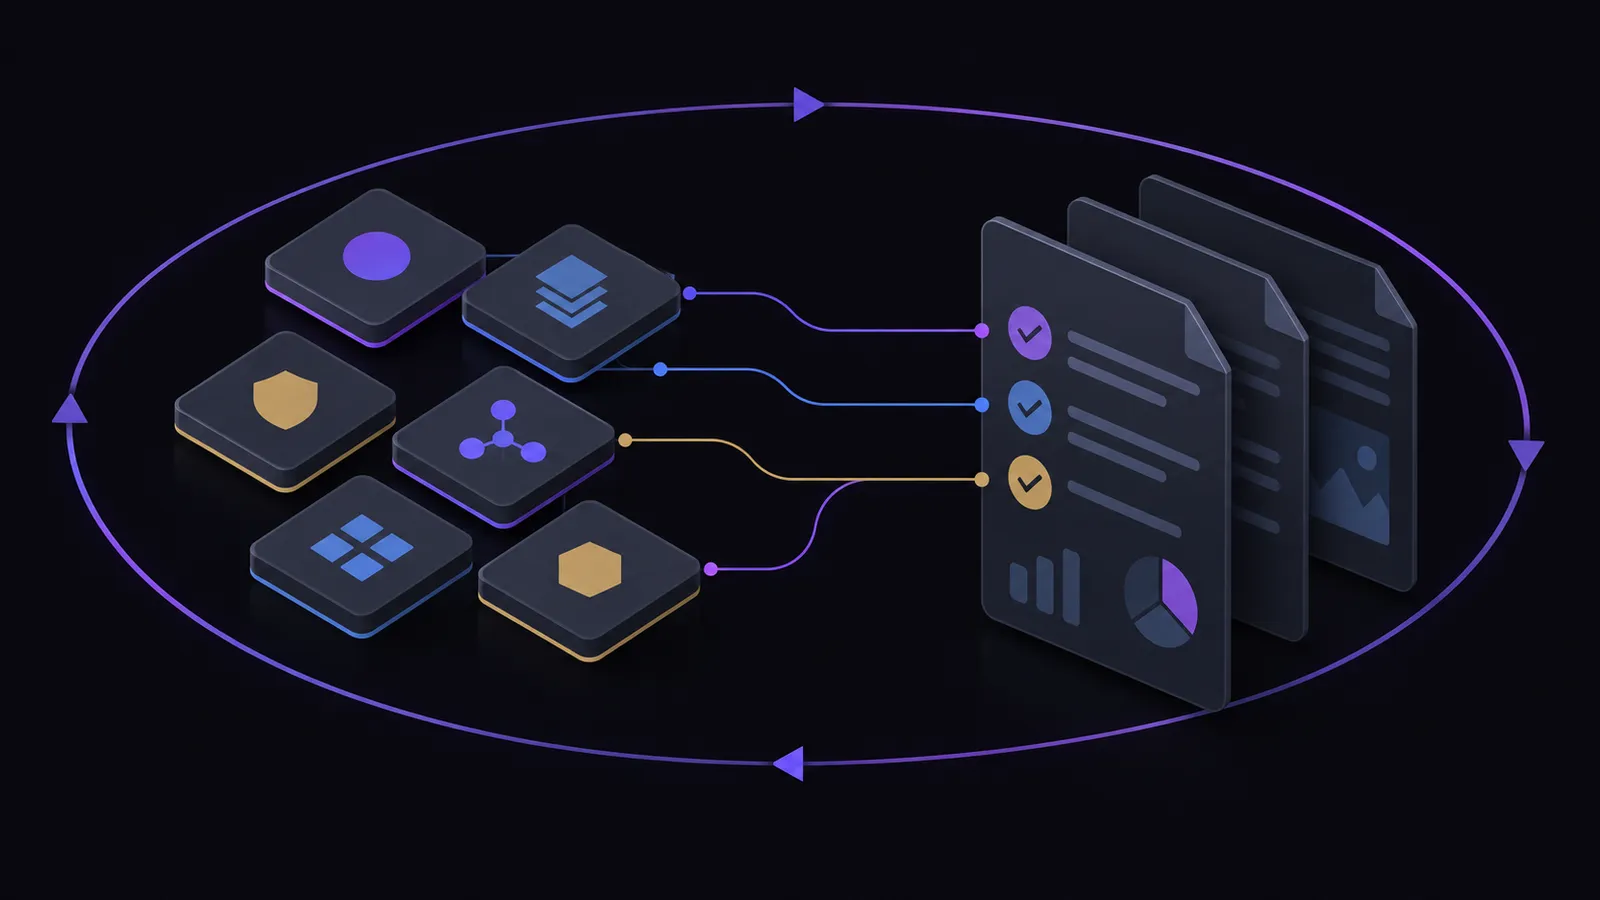
Legacy GRC tools digitized the spreadsheet. We replaced the process entirely. Autonomous GRC means AI agents that continuously sense, decide, act, and verify : so your compliance posture is always current, never stale.
Sense
Agents continuously scan your infrastructure, configs, access logs, and third-party tools for control status.
Decide
AI evaluates findings against your compliance frameworks, risk appetite, and organizational policies.
Act
Automated remediation patches misconfigurations, revokes excess permissions, and triggers workflows.
Verify
Every action is logged with tamper-proof evidence. Continuous validation confirms the fix actually worked.
Why This Is Inevitable
Regulatory pressure is accelerating: SEC cyber rules, DORA, NIS2, new state privacy laws. At the same time, AI agents have reached the maturity to reliably monitor and act on complex compliance logic. The window between "manual GRC" and "autonomous GRC" is closing fast. Early movers gain audit confidence. Late movers inherit risk.
Three Steps. Zero Spreadsheets.
Start continuous compliance without a months-long implementation.
Connect
Plug into your existing stack. No agents to install, no architecture changes.
- AWS, Azure, GCP native integrations
- Identity providers (Okta, Azure AD)
- Endpoint tools (CrowdStrike, SentinelOne)
- Ticketing (Jira, ServiceNow)
- 600+ integrations out of the box
Monitor
AI agents validate every control, every hour: not every quarter.
- Continuous control validation
- Real-time drift detection
- Automated gap analysis
- Cross-framework mapping
- Risk-prioritized alerting
Prove
When your auditor asks for evidence, it's already there: timestamped and verified.
- Auto-generated evidence packages
- Tamper-proof audit trails
- One-click auditor export
- Framework-specific report templates
- Continuous readiness scoring
Everything Your GRC Team Needs. Nothing They Don't.
Risk Register
Always current. Never a guessing game.
Your risk register updates itself from live infrastructure data, threat intelligence, and control status. No more quarterly manual reviews that are outdated the day they're published.
Evidence Collection
Collected before you ask for it.
Screenshots, logs, configurations, and access reviews: captured automatically, timestamped, and mapped to controls. Your team stops chasing artifacts and starts focusing on security.
Compliance Mapping
One control. Every framework. Automatically.
AI maps your controls across SOC 2, ISO 27001, NIST, GDPR, HIPAA, and PCI DSS simultaneously. Implement once, satisfy many: without a consultant and a crosswalk spreadsheet.
Document Repository
Questionnaires answered in minutes, not weeks.
Security questionnaires, vendor assessments, and policy documents auto-populated from your actual environment. Responses are accurate because they're generated from live data, not last quarter's memory.
Remediation Playbooks
Fixes that execute themselves.
When a control fails, the platform doesn't just alert you: it fixes the issue. Auto-patching for cloud misconfigurations, access anomalies, and policy violations with full rollback capability.
Audit Readiness Dashboard
Know your score before the auditor does.
A real-time compliance score across every framework you care about. Drill into any control to see status, evidence, owner, and remediation history: all in one place.
What Changes When Compliance Runs Itself
How the work changes when agents monitor controls and collect evidence around the clock.
Data model
From framework requirement to automated evidence, in one linked chain.
A GRC platform is software that maps framework requirements to controls, tests those controls, stores the evidence and reminds owners when something slips. Hunto keeps every link live.
- 01
Requirement
A clause from SOC 2, ISO 27001, HIPAA, DORA or another framework.
- 02
Control
One control can satisfy requirements across many frameworks.
- 03
Automated check
Agents test the control against your live systems.
- 04
Evidence
Timestamped records are stored against the control.
- 05
Reminder
Owners are nudged when evidence is stale or a check fails.
What Is a GRC Platform?
Governance, risk, and compliance software.
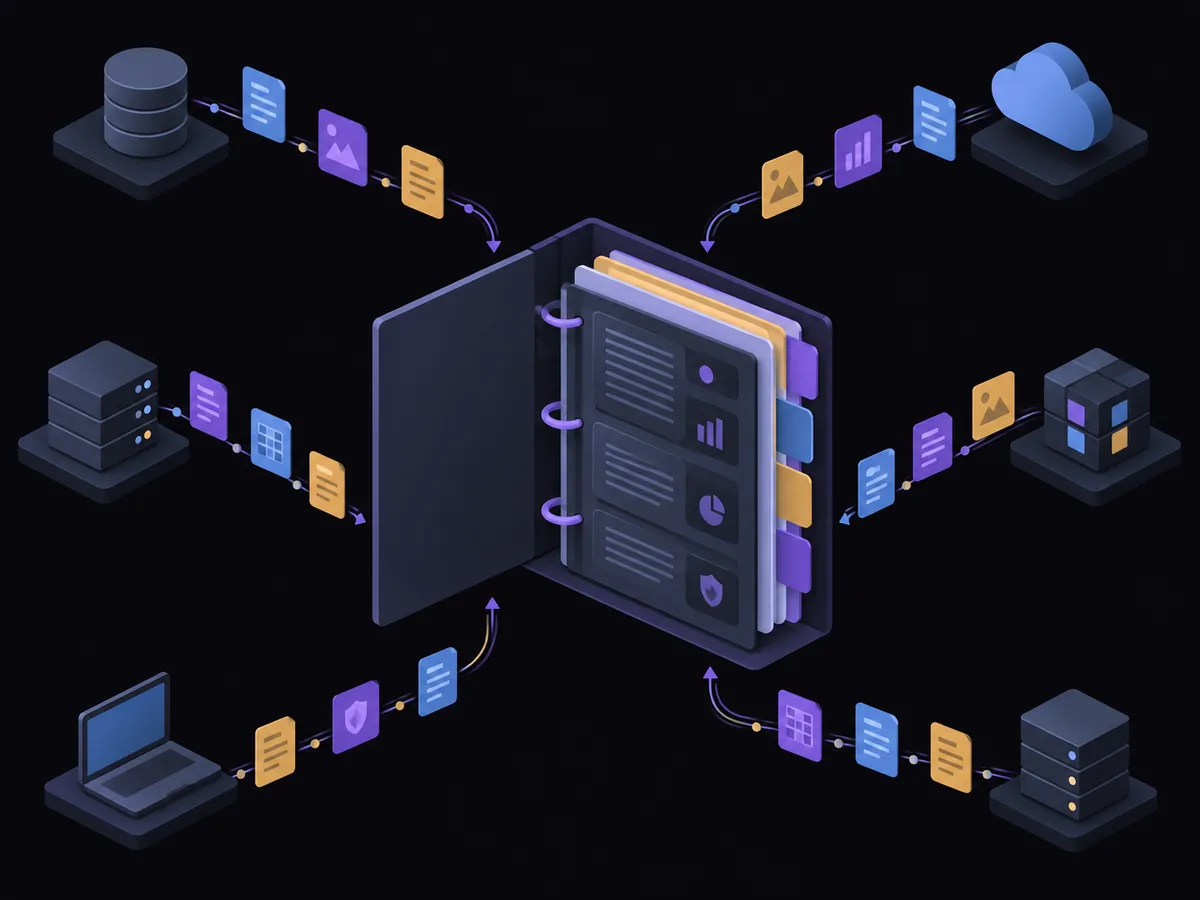
A GRC platform is software that brings governance, risk management, and compliance into one system, mapping controls to frameworks like SOC 2, ISO 27001, HIPAA, PCI DSS, GDPR, and RBI and tracking the evidence.
First-generation tools digitised the spreadsheet, second-generation tools (Vanta, Drata, Sprinto) automated monitoring, and third-generation autonomous GRC, Hunto's approach, remediates issues and proves the fix with tamper-proof evidence.
GRC Platform vs. Manual Compliance
Specific time, cost, and coverage improvements when you move from manual processes to a GRC platform.
| Dimension | GRC Platform (Hunto) | Manual / Spreadsheet |
|---|---|---|
| Audit Preparation | Fast: evidence already collected and mapped | 6–8 weeks of manual scrambling across teams |
| Evidence Freshness | Real-time: captured continuously with timestamps | Stale within days of collection |
| Control Visibility | Controls monitored continuously in real time | ~60% coverage, checked quarterly at best |
| FTE Cost | Oversight only: AI handles operational work | 3–5 FTEs dedicated to compliance ops |
| Audit Findings | 0–2 per cycle: drift caught and fixed in real time | 12–15 findings per cycle on average |
| Multi-Framework Overhead | Cross-mapped automatically: one control satisfies many | Each framework tracked separately with duplicated effort |
| Remediation Speed | Minutes: autonomous playbooks with rollback | Days to weeks: manual tickets, engineer queues |
A GRC platform like Hunto saves money through lower consulting fees and freed engineering time.
The Problem with Traditional GRC
Traditional GRC was built for annual audits, so evidence goes stale, risk registers lag, and engineers spend 30% or more of their time gathering screenshots. First-generation tools digitised the spreadsheet but not the process.
A modern GRC platform must act autonomously, which is why teams are rethinking AI in cybersecurity and compliance.
What Makes an Autonomous GRC Platform Different?
An autonomous GRC platform runs a closed loop: Sense → Decide → Act → Verify. Every other approach needs a human to bridge a gap.
Continuous Control Monitoring
Drift is detected within minutes, not at audit prep.
Automated Evidence Collection
Screenshots, configs, and access logs are captured, timestamped, and mapped to every framework.
Cross-Framework Mapping
One control satisfies overlapping requirements, such as encryption at rest in SOC 2 CC6.1, ISO 27001 A.10.1, HIPAA 164.312(a)(2)(iv), and PCI DSS 3.4.
Autonomous Remediation
Pre-approved playbooks fix control failures, with every action logged and reversible.
Risk Register Auto-Updates
In an autonomous cyber risk management platform, scores update from live data and attack surface management.
Hunto vs Traditional GRC Platforms
For Vanta alternatives and Vanta competitors, here is how Hunto compares.
| Feature | Hunto | Vanta | Drata | Sprinto |
|---|---|---|---|---|
| Autonomy level | Autonomous (Sense → Decide → Act → Verify) | Monitor + alert | Monitor + alert | Monitor + alert |
| Control monitoring | Continuous (real-time) | Periodic checks | Periodic checks | Periodic checks |
| Evidence collection | Automated + tamper-proof timestamps | Automated screenshots | Automated screenshots | Automated screenshots |
| Framework coverage | 12+ (incl. DPDP, DORA, NIS2, SEC) | SOC 2, ISO, HIPAA, GDPR, PCI | SOC 2, ISO, HIPAA, GDPR, PCI | SOC 2, ISO, HIPAA, GDPR |
| Remediation | Autonomous with rollback | Manual (ticket created) | Manual (ticket created) | Manual |
| Cross-framework mapping | AI-driven, automatic | Basic | Basic | Limited |
| Cyber risk integration | Native (ASM, DRP, threat intel) | None | None | None |
| Deployment | Cloud, on-prem, hybrid | Cloud only | Cloud only | Cloud only |
Vendor columns describe general positioning of first-generation compliance automation tools and are not a verified feature audit. Capabilities change, so check each vendor's current documentation before deciding.
A Drata alternative or Sprinto alternative that closes the loop: one continuous compliance platform.
Compliance Frameworks Supported
Hunto's compliance automation software supports 12+ frameworks with cross-mapped controls and continuous evidence collection.
SOC 2 Type II
SOC 2 automation monitors the Trust Services Criteria across the 6-12 month observation period. Compare tools in our guide to SOC 2 compliance automation tools.
ISO 27001
An ISO 27001 compliance tool that maps controls to the 93 Annex A controls, with live evidence in the Statement of Applicability.
HIPAA
Monitors access, encryption, audit logging, and training for PHI safeguards.
PCI DSS
Monitors all 12 PCI DSS v4.0 requirement families continuously, as QSAs now expect.
GDPR
Keeps an always-current record of processing, consent, and data subject requests.
NIST CSF & NIST 800-53
Maps your environment against NIST CSF 2.0 and 800-53 Rev 5 together.
CIS Controls
Validates CIS v8 implementation groups IG1 to IG3 across all 18 control families.
DPDP Act, SEC Cyber Rules, DORA & NIS2
Covers India's DPDP Act, SEC disclosure rules, DORA, and NIS2, often the same controls as DMARC compliance.
RBI Cybersecurity Guidelines
Monitors RBI-specific controls and generates the logs, incident documentation, and board reporting examiners require, mapped alongside SEBI and IRDAI.
Autonomous GRC for Regulated Industries
Continuous compliance for sector-specific mandates.
Banking & Financial Services
Monitors RBI, SEBI, and SEC controls together, with phishing simulation for the human-risk component.
Healthcare
Monitors HIPAA Security Rule safeguards and BAA compliance without involving clinical staff.
E-commerce & Retail
Validates PCI DSS v4.0 segmentation, encryption, access, and logging in real time.
Government & Critical Infrastructure
Covers NIST 800-53, CMMC, and NIS2, with on-premise deployment so data stays in your perimeter.
SOC 2 Compliance Software That Keeps You Audit-Ready
Hunto is SOC 2 compliance software for SaaS and mid-market teams: a SOC 2 automation platform that maps your controls, collects evidence continuously and shows audit progress in one place, so Type I and Type II readiness is a status, not a project.
Continuous SOC 2 monitoring
Agents test controls against your cloud, identity and code tools every day and flag drift before an auditor does.
Audit progress you can track
Each Trust Services Criterion shows control status, evidence coverage and open gaps, with owners and due dates.
Compliance reporting for SaaS
Auditor-ready exports and a shareable trust view replace screenshots and spreadsheet trackers.
One control, many frameworks
Evidence collected for SOC 2 is reused for ISO 27001, HIPAA and the other frameworks through cross-framework mapping.
Comparing SOC 2 compliance automation software? Read our SOC 2 compliance automation tools roundup, or book a demo to see your own controls mapped.
GRC Platform for Mid-Market Companies
Enterprise-grade automation, mid-market price.
Hunto gives mid-market teams SOC 2 and ISO 27001 readiness without a dedicated GRC team: 600+ integrations, no six-month implementation, and one person overseeing the programme.
Adding a framework takes days via cross-framework mapping. See the pricing page, book a demo, or pair GRC with the autonomous SOC.
Integration Ecosystem: 600+ Connections Out of the Box
Hunto connects to your entire stack.
Cloud Infrastructure
AWS, Azure, GCP, DigitalOcean
Identity & Access
Okta, Azure AD, Google Workspace, OneLogin
Endpoint Security
CrowdStrike, SentinelOne, Carbon Black
Ticketing & Workflow
Jira, ServiceNow, Linear, Asana
Code & DevOps
GitHub, GitLab, Bitbucket, Jenkins
Communication
Slack, Microsoft Teams, PagerDuty
HR & People
BambooHR, Rippling, Gusto, Workday
MDM & Devices
Jamf, Kandji, Intune, Mosyle
Monitoring & SIEM
Datadog, Splunk, Sumo Logic, Elastic
Integrations are pre-built (OAuth or API key) and pull control data within minutes. A REST API and webhooks cover anything else.
Free compliance checklists and guides
Framework-by-framework working documents from the Hunto compliance library.
Frequently Asked Questions
Everything you need to know about our Autonomous GRC Platform
Your Next Audit Is Closer Than You Think
Get a free 48-hour Compliance Readiness Assessment. We'll connect to your environment and show you exactly where your gaps are: with evidence and a remediation plan.
No credit card. No sales pitch. Just a clear picture of your compliance posture delivered by autonomous AI agents.