Defend Client Privilege,
Secure Your Practice
Protect privileged data. Stay audit-ready at all times. Autonomous threat detection, dark web intelligence, and compliance automation: purpose-built for law firms, barristers, and legal service providers.
Trusted by enterprises and security teams
Short answer
24/7
agent coverage on your external footprint
ISO 27001:2022
certified by BSI. SOC 2 is in progress
12+
compliance frameworks supported
150+
enterprise customers
How Hunto Works
Go from zero to fully protected in days. Zero disruption to case work or client service.
- 1
Confidential consultation
We assess your firm's IT environment, data handling practices and compliance obligations to design a tailored security programme.
- 2
Custom agent configuration
Agents for client portals, email systems, document management exposure, dark web and vendor security.
- 3
Deployment and continuous protection
Agents go live quickly with 24/7 detection, automated remediation and compliance dashboards, without accessing any privileged data.
AI Agents for Law Firm Security & Compliance
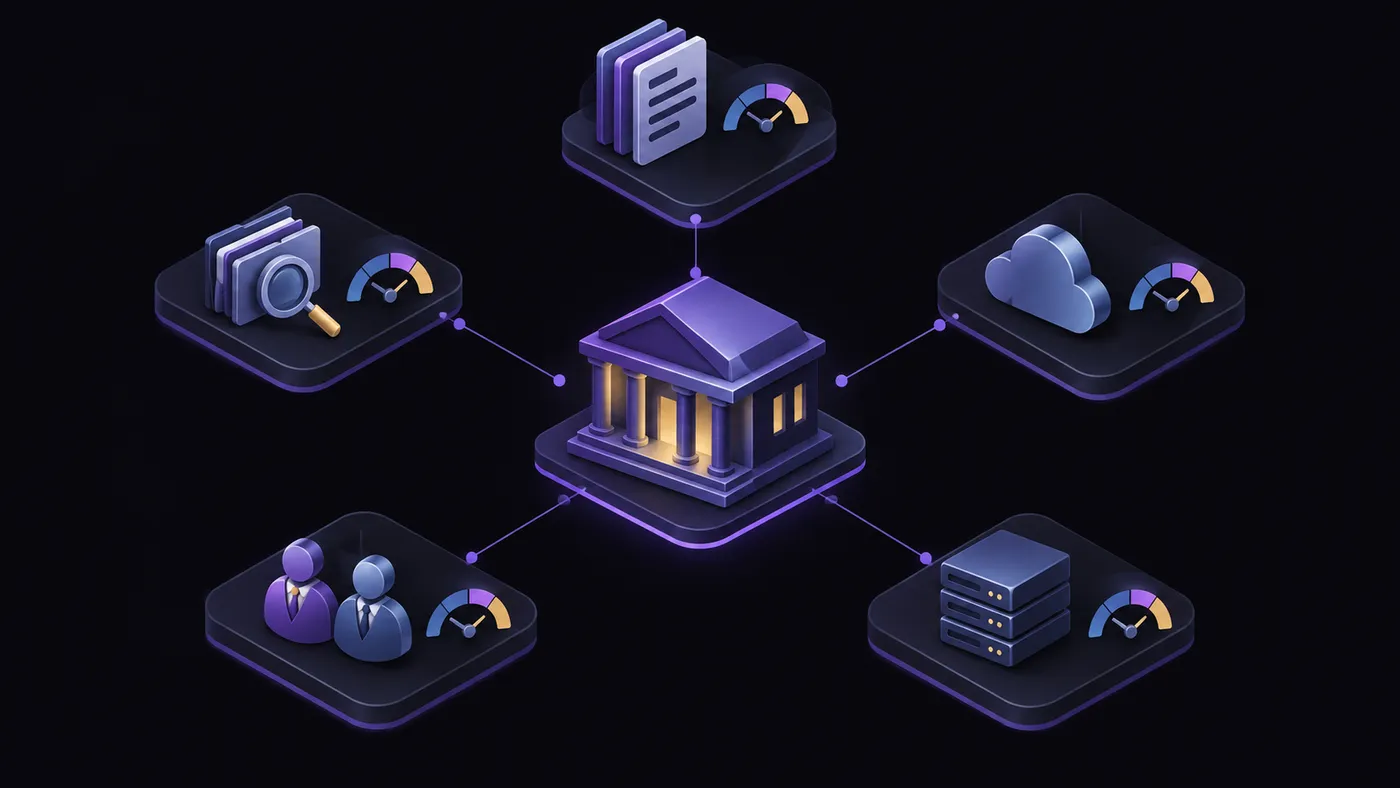
Every module is designed for the threat landscape of the legal industry, from client privilege protection to vendor due diligence.
Attack Surface Management
Continuously discover and monitor your firm's internet-facing assets: client portals, document management systems, email servers, and cloud infrastructure.
DMARC+ Email Security
Protect attorney-client communications from email spoofing, phishing, and interception. Enforce DMARC, SPF, and DKIM across all firm domains to prevent business email compromise.
Dark Web Monitoring
Detect leaked client data, attorney credentials, and confidential case materials on dark web forums before they can be exploited.
Third-Party Risk Monitoring
Assess the security posture of legal tech vendors, e-discovery platforms, cloud storage providers, and co-counsel firms you share data with.
Human Risk Management
Tailored phishing simulations and security awareness training for attorneys, paralegals, and administrative staff: protecting against social engineering.
Brand & Fraud Protection
Detect impersonation of your firm's partners, fraudulent legal services, and phishing campaigns targeting your clients.
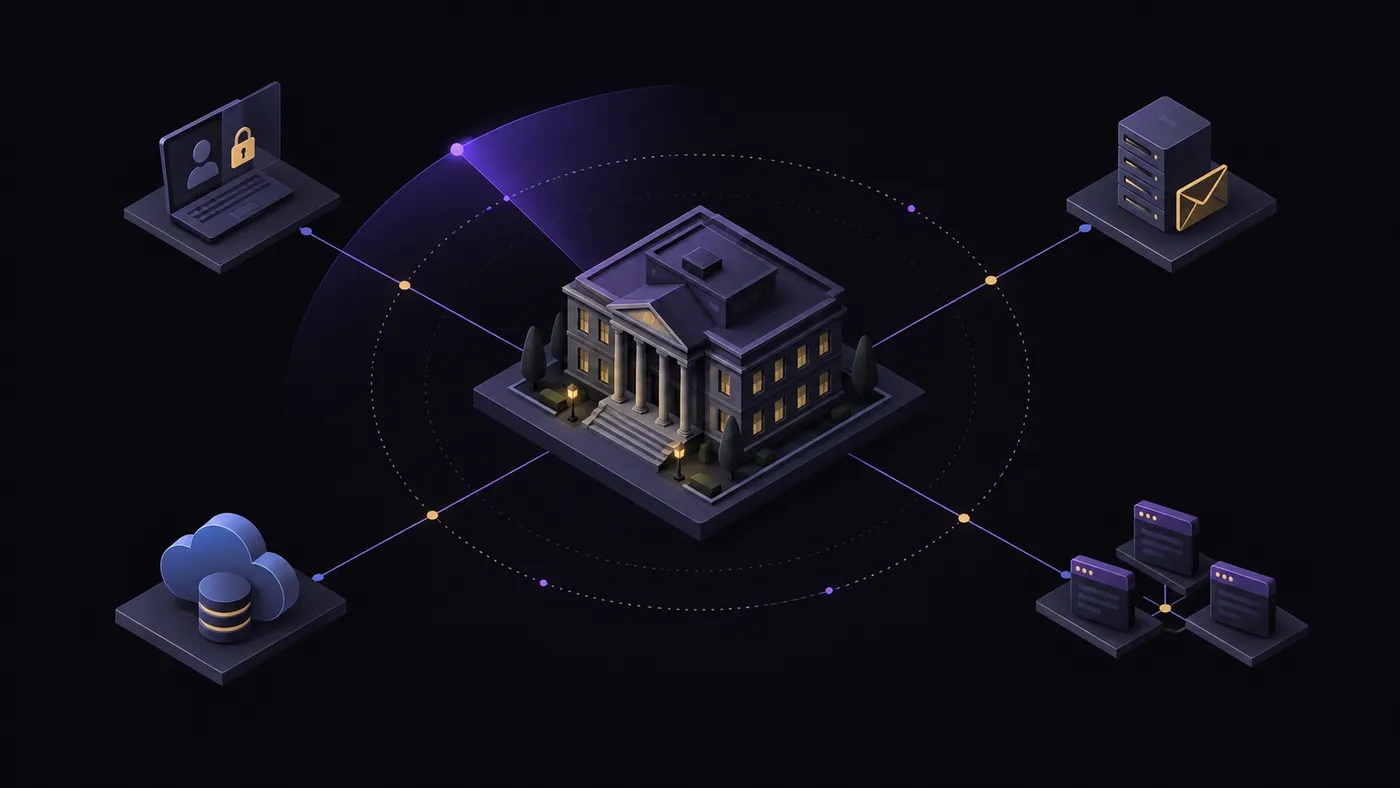
Network Monitoring for Law Firms: Watching the Perimeter You Can't See
Internal tools watch inside the firewall. The breaches that make headlines usually start outside it.
| Where it happens | Internal network monitoring | Hunto external monitoring |
|---|---|---|
| Client portal and VPN exposure | Sees traffic that reaches it | Discovers and monitors the internet-facing login pages and endpoints |
| Forgotten subdomains from old matters | Not on the inventory, so not watched | Found by attack surface discovery |
| Spoofed or look-alike domains | Outside your network, so invisible | Detected, then taken down |
| Leaked attorney credentials | Appear only once used | Dark web and breach monitoring alerts early |
| Legal tech and cloud vendors | Vendor-side posture is out of view | Third-party risk monitoring |
| Activity inside the firewall | Core strength (SIEM, EDR, firewall logs) | Not covered. Keep your internal tools |
Hunto provides the external half of network monitoring for law firms: continuous attack surface monitoring, dark web monitoring for leaked credentials, and impersonation detection, with verified alerts and automated takedowns.
Why Law Firms Are High-Value Cybersecurity Targets
Law firms aggregate secrets from many organisations, so one breach can trigger regulatory action and malpractice claims.
Aggregated secrets
M&A strategy before announcement, litigation playbooks, IP filings and privileged communications from many organisations in one place.
Motivated attackers
Economic espionage, ransomware groups that expect urgency to restore operations, and social engineers who exploit trust-based legal communications.
Thin defences
Many practices still rely on basic antivirus and firewalls. Hunto adds autonomous, enterprise-grade monitoring that does not disrupt legal workflows.
Protecting Client Confidentiality and Attorney-Client Privilege
ABA Model Rule 1.6(c) asks lawyers to make reasonable efforts to prevent unauthorized disclosure of client information. Hunto protects confidentiality without ever accessing privileged data, working only at the perimeter.
Dark web monitoring
Agents scan underground forums, paste sites and marketplaces for leaked client data, attorney credentials and mentions of your firm in breach databases, giving early warning before privileged information is weaponised.
ABA Cybersecurity Guidelines and Ethical Compliance for Law Firms
Rule 1.6(c): reasonable efforts
Lawyers must make reasonable efforts to prevent inadvertent or unauthorized disclosure of, or access to, client information.
Opinion 477R: secure communications
Reasonable efforts to secure electronic client communications, including strong authentication, encryption where warranted and vendor due diligence.
Client requirements
Corporate clients, financial institutions and government agencies increasingly send security questionnaires to outside counsel and ask for SOC 2 or ISO 27001 evidence.
Hunto's GRC Autopilot generates SOC 2, ISO 27001 and GDPR evidence packages. Hunto holds ISO 27001:2022 certification (BSI); its SOC 2 programme is in progress. This page is general information, not legal advice.
Sources: ABA Model Rule 1.6 · ABA Formal Opinion 477R · SRA Code of Conduct for Solicitors. UK firms: confidentiality is also covered by paragraph 6.3 of the SRA code.
Email Impersonation and Business Email Compromise in Law Firms
Attackers impersonate partners or clients to redirect wire transfers, especially closing funds in real estate and M&A matters.
DMARC+ Email Security enforces SPF, DKIM and DMARC, and Takedown removes look-alike domains. See also business email protection and what is DMARC.
Phishing Simulation and Security Training for Legal Professionals
Realistic legal lures
Fake court notices, bogus client instructions, impersonated opposing counsel and fraudulent document-sharing links.
Training after every click
Each simulation is followed by targeted training that teaches staff to identify and report suspicious messages.
Adaptive difficulty
Simulations adapt to each person's risk profile, with harder scenarios for repeat clickers, instead of one annual course.
Delivered by Human Risk Management and AI phishing simulation. Background: security awareness training.
Compliance Frameworks for Law Firms
Meet client security expectations and regulatory requirements with checklists, guides and frameworks tailored for the legal industry.
SOC 2 Type II Readiness
Compliance guide for law firms seeking SOC 2 certification: increasingly required by corporate clients and insurers.
ISO 27001:2022 Implementation
Information security management checklist for law firms handling confidential client data and privileged communications.
GDPR Compliance Checklist
Data protection compliance for law firms processing EU client data: consent management, data retention, and cross-border transfer rules.
DPDPA (India) Compliance
India's data protection requirements for law firms handling personal data of Indian clients and entities.
CERT-In Compliance Guide
Incident reporting and cybersecurity compliance obligations for law firms operating in India.
CPS 234 Information Security
Information security checklist for Australian law firms handling regulated client data.
Cybersecurity for Law Firms: FAQs
Common questions about securing law firms and protecting client privilege with Hunto
Protect Your Firm & Your Clients
Book a confidential demo to see how Hunto's autonomous agents safeguard attorney-client privilege and sensitive legal data 24/7.
